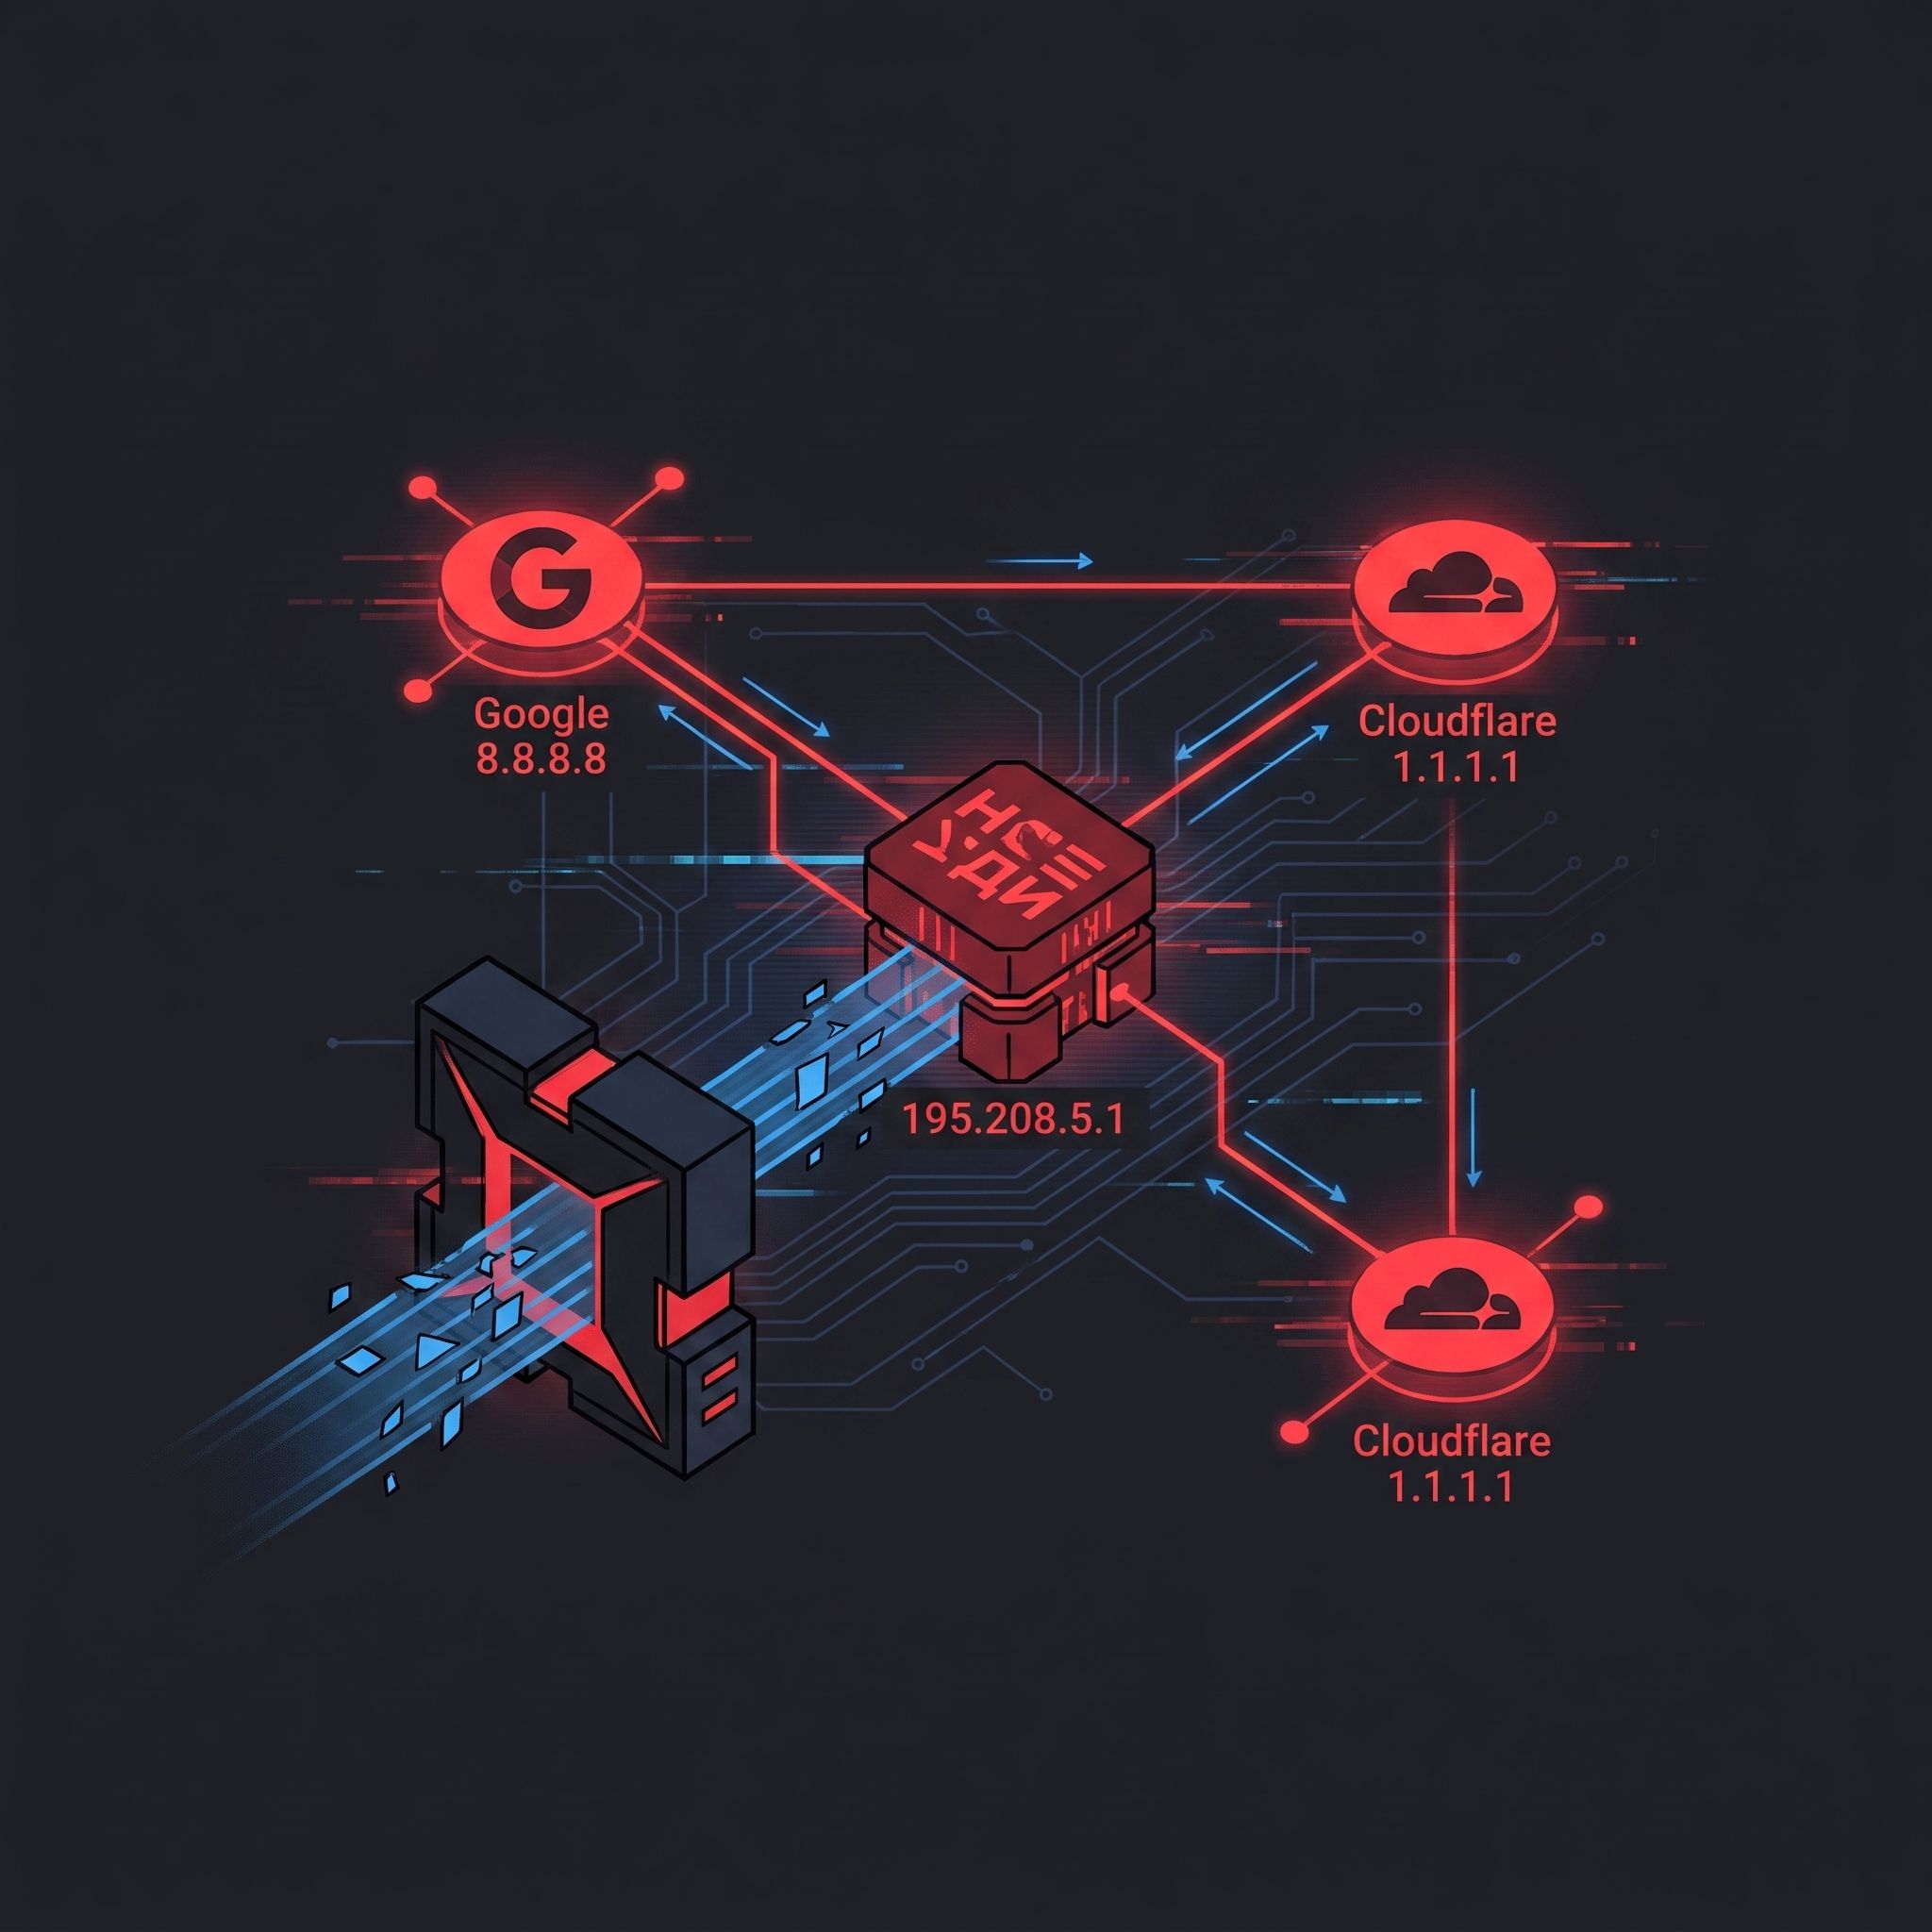
Starting on the evening of August 26, 2026, a new interference with network traffic was detected in Russia. Specialized TSPU equipment began intercepting unencrypted DNS requests sent to popular public servers owned by Google (8.8.8.8) and Cloudflare (1.1.1.1). Previously, secure DoH protocols from these companies had already been blocked on the same nodes.
Technical analysis shows that when attempting to resolve the IP address of a blocked resource, the system instantly returns an error stating that the domain does not exist. This interception only affects traffic sent over the UDP protocol. If requests are sent using TCP, the servers still return correct and genuine IP addresses.
Technical details of the redirection system
Network tests revealed an interesting detail: changing the time-to-live (TTL) parameter of packets can bypass the filtration. Sending an initial request with a low TTL and then repeating it with a normal value results in receiving the original IP address. This bypass does not work when sending random packets that do not contain DNS queries.
Specialists determined that destination address spoofing occurs during interception. The traffic is redirected to the servers of the National Domain Name System (NSDI). Consequently, telecom operators see connections to the NSDI IP address 195.208.5.1 instead of the original Google or Cloudflare servers.
Potential reasons for the changes
Experts suggest that this measure might have been introduced to alleviate the load on TSPU hardware. Preventing the successful resolution of blocked domains eliminates the need for the system to analyze subsequent encrypted user traffic, thereby saving computing resources.
Using a reliable service like HiroVPN helps bypass such restrictions and protects your DNS requests from being intercepted or spoofed by internet providers.