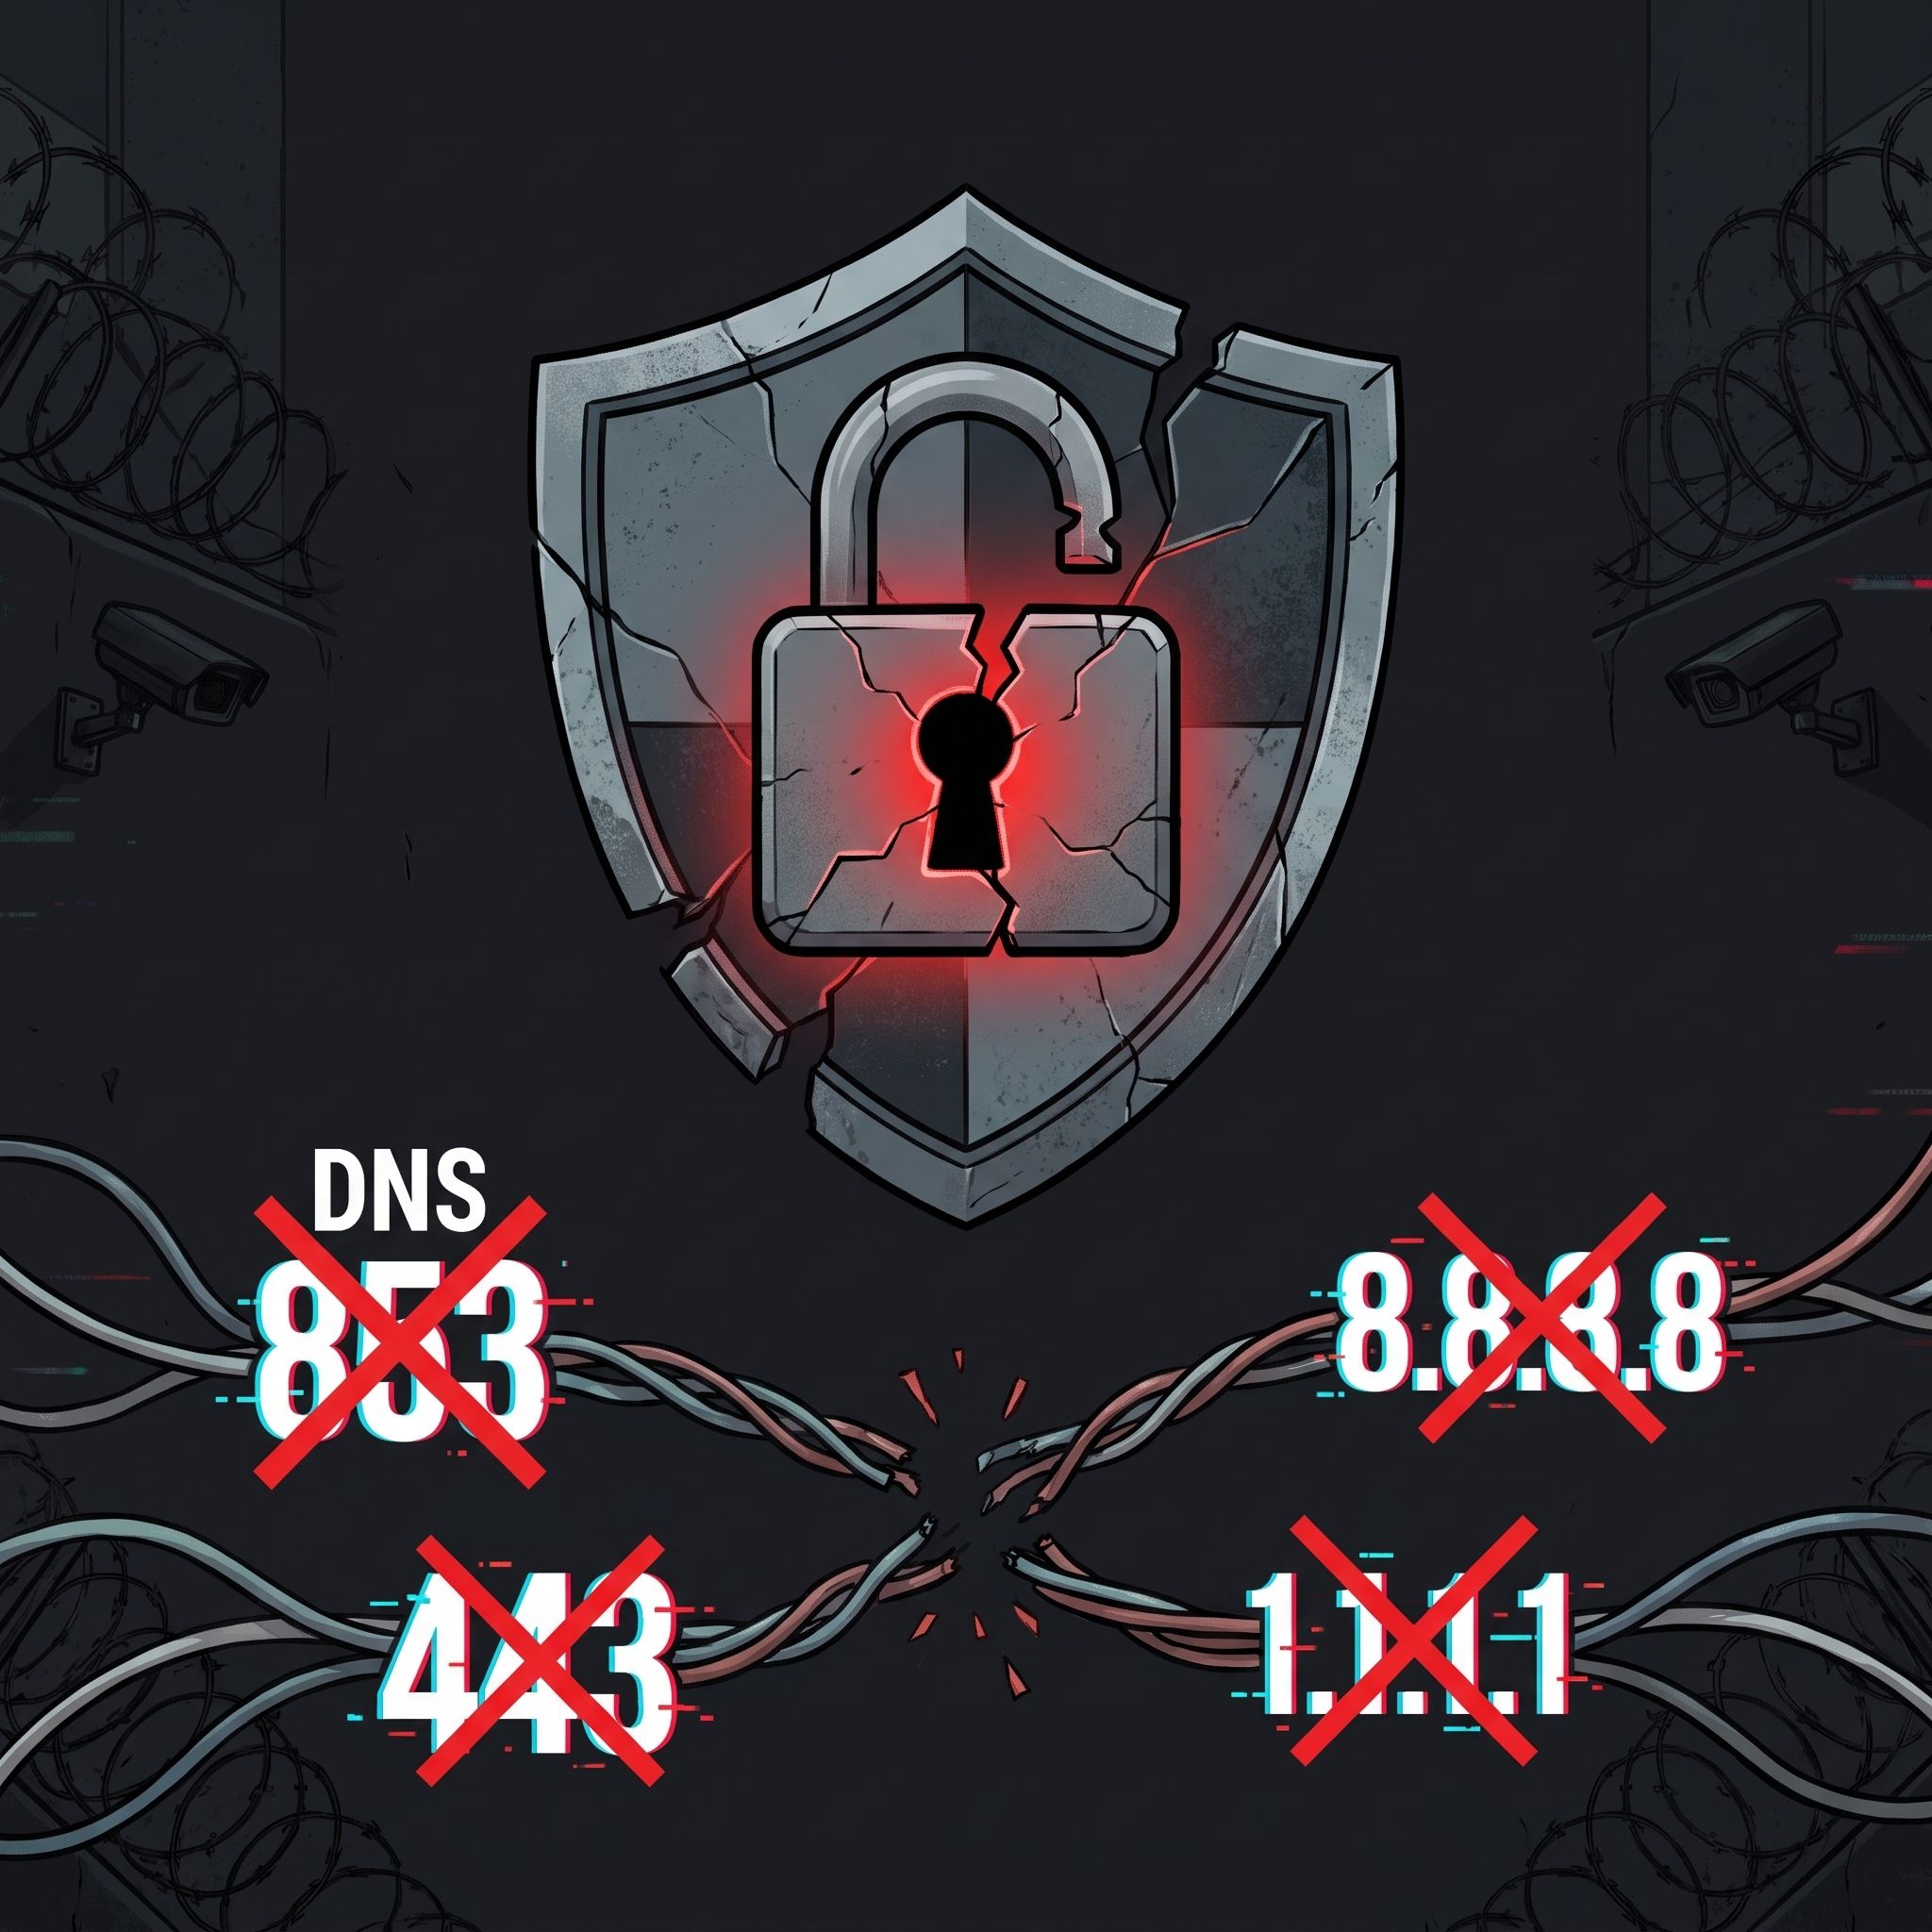
In late August 2026, Russian internet users experienced disruptions in the operation of encrypted DNS services from Google and Cloudflare. The issue affected subscribers of several major providers, including Rostelecom, Beeline, Dom.ru, Tattelecom, and SkyNet. Technical specialists noted that requests to the secure DoT and DoH protocols stopped receiving responses, with the nature of the failures varying depending on the technology used.
What is the difference between DoT and DoH technologies
Regular DNS requests are sent in clear text via port 53, allowing telecom operators to easily intercept and manipulate data. To protect against this, two technologies are used. DoT encrypts traffic inside a TLS tunnel through a dedicated port 853. DoH masks DNS requests as standard HTTPS web traffic, sending them over port 443 along with regular websites.
How exactly the blocks are carried out
Analysis of network traffic showed different methods of restricting access. When attempting to use DoT, the connection is reset immediately after the TCP session is established using a special RST flag. With the DoH protocol, the situation is different: the client sends a hello packet, but the DPI traffic filtering system simply ignores subsequent packets, causing the connection to time out. Filters identify requests by the server name in the unencrypted SNI field.
Forced redirected traffic and DNS spoofing
In addition to blocking encrypted protocols, instances of intercepting regular unencrypted DNS traffic have been recorded. Requests to Google servers with IP addresses 8.8.8.8 and Cloudflare with 1.1.1.1 are forcibly redirected to the National Domain Name System. As a result, users receive fake responses stating that blocked websites do not exist, although the requests themselves do not physically reach the destination servers. This can be verified by technical markers in the responses or using special traceroute tools.
Possible ways to bypass the restrictions
To restore functionality, users employ alternative methods of bypassing deep packet inspection or send requests directly to IP addresses without specifying the domain name in the SNI. However, the most reliable and stable solution remains routing all traffic, including DNS queries, through an encrypted virtual tunnel. In this scenario, the provider's filtering systems cannot identify and block individual requests to name servers.
With the HiroVPN service, users are reliably protected from such blocks and DNS interception because all traffic is fully encrypted inside a stable tunnel.